Digital Employees and Agents — Safe to Admit to Databases, Code, and Funds
Autonomous agents automate accounting, legal review, and software delivery inside enterprise systems. Before any tool call runs, the MITR action gate proves admissibility in 1.08 ms on a standard processor and records a cryptographic audit receipt.
SHA-256 receipts (55 epochs as of 15 November 2026); epoch 33 anchored via OpenTimestamps
Interactive MITR deterministic gate simulator
Client-side predicate evaluation + live WebCrypto SHA-256 receipt chainChief Information Security Officers and AI architects
Enforce deterministic bounds on Model Context Protocol (MCP) tools, Structured Query Language (SQL) writes, and enterprise resource planning (ERP) connectors without sending secrets to external clouds.
Formal methods and security researchers
Reproduce 5,079 historical epoch-33 receipt decisions (5,373 live chain records across 55 epochs as of 15.11.2026), inspect Apache-2.0 client packages, and review the 157-scenario adversarial benchmark and Invariant, Nondestructive, Deterministic Resilience Audit (INDRA) protocol measured on the internal reference stand prior to external accredited laboratory trials.
DeepTech investors and strategic partners
Examine the zero-GPU unit economics, two-contour special-purpose vehicle (SPV) equity with 25% gross-revenue payback, two 2026 patent filings, and 856-page monograph.
Three generations of enterprise control over software agents
| Engineering dimension | Generation 1 · Static API gateways & role-based access control (RBAC) | Generation 2 · Probabilistic LLM guardrails (NeMo, Llama Guard, Lakera) | Generation 3 · Pre-execution SMT action gate (ISSLAB MITR) |
|---|---|---|---|
| Object inspected | Network endpoint and static role token under RBAC | Natural-language prompt and completion surface phrasing | Structured tool call, typed parameters, target state, and credential custody |
| Decision mechanism | Static route allowlist without payload semantics | Secondary neural classifier estimating probability of harm | Deterministic Satisfiability Modulo Theories (SMT) proof in the Microsoft Research theorem prover (Z3) over QF_UFLIA |
| Latency & compute | < 1 ms CPU (blind to business invariants) | 250–800 ms on graphics processing unit (GPU) per call | 1.08 ms warm median on standard 4-core CPU (zero GPU tokens) |
| Indirect prompt injection | Passes any destructive call permitted to the service account | Susceptible to paraphrase, encoding, and multi-turn framing | Invariant to prompt wording; blocks any call lacking a formal proof |
| Refusal feedback & audit | Hypertext Transfer Protocol (HTTP) 403 status code; mutable application log | Opaque confidence score; no mathematical witness | Exact violated clause (Unsat Core) + OpenTimestamps SHA-256 receipt chain |
OWASP Top 10 for Agentic Applications (ASI01–ASI10) coverage
| Agentic risk class | Failure mode without deterministic gate | Information Security 3.0 control (MITR Z3 + INDRA Field Edition) |
|---|---|---|
| Goal Hijack & Context Poisoning (ASI01, ASI06) | Indirect instructions inside documents or retrieval corpora redirect agent actions | Typed tool-call Z3 invariants enforce fixed scopes independent of prompt prose; INDRA probes INDR-09–INDR-14 |
| Tool Misuse & Unexpected Execution (ASI02, ASI05) | Excessive parameters, destructive filesystem writes, or arbitrary shell execution | QF_UFLIA parameter bounds, path denylists, and container allowlists checked in 1.08 ms prior to execution |
| Identity Abuse & Supply Chain (ASI03, ASI04) | Raw credentials inside prompt context or compromised public Python packages | Zero-trust credential custody held inside MITR gate; offline SHA-256 pinned wheels (--no-index) |
| Cascading Errors & Rogue Autonomy (ASI07–ASI10) | Unbounded retries, unverified inter-agent trust, and mutable logs lacking accountability | Unsat Core counterexamples, 3-retry circuit cap, and OpenTimestamps SHA-256 audit chain (5,373 records) |
Start a 14-day INDRA assessment, 30-day MITR pilot, or investor briefing
Select the engagement track and enter a work address to submit a structured engineering or diligence brief directly over Transport Layer Security (TLS) to isslab.ai. Zero cookies and zero third-party processors are involved; details are published in the privacy policy.
Select a role and task
Eight direct routes through the solutions and knowledge base of the institute: from deploying digital employees inside an accounting contour to independently verifying the cryptographic receipt chain.
Business owner and chief executiveHow to entrust contracts, accounting, and estimates to digital employees without risk
Domain assistants and autonomous agents connect to corporate accounting and legal systems under formal admission rules. Trade secrets remain inside the perimeter, and every action is checked before execution.SolutionsDigital employeesProcedurePilot at a customerChief technology officer and developerHow to install the gateway in five minutes and protect databases from coding-agent errors
The median rule-evaluation time on a standard server processor is 1.08 milliseconds (measured on 24 October 2026 across 1,000 decisions). The trial package installs offline in five minutes.StartInstall in five minutesArchitectureFormal verificationHead of information securityWhat is blocked, where the gateway sits, and what remains inside the perimeter
The gateway operates inside the protected customer perimeter on a standard processor without graphics accelerators or internet egress. Formal rules, the receipt log, and cryptographic keys stay with the customer.GatewayMITR action controlRequirementsRules and liabilityLegal counsel and compliance specialistWhich legal rules govern autonomous agents and how to protect company directors
Translation of corporate fiduciary duties, personal-data statutes, and critical-infrastructure protection standards into machine-readable admission rules and an evidentiary receipt chain containing no personal data.OverviewWho is liableAnalysisRules and liabilityPartner and systems integratorHow to embed governed agents and the MITR gateway into enterprise client projects
Joint deployment of domain contours and protection of large language models inside partner client perimeters: a thirty-day observation pilot, tool-call dictionary mapping, and regulatory audit readiness.ModelPartners and integratorsProcessPilot at a customerInvestor and grant committeeWhat already runs in production, how it is measured, and how the product line scales
MITR has operated continuously since 24 April 2026: 20 of 20 rules in enforce mode and 157 of 157 attack scenarios and routine calls decided accurately on the internal reference testbed prior to external laboratory accreditation (snapshot of 24 October 2026). Every metric carries a date and a replay command.SummaryInvestors and partnersDocumentMemorandum 2.0 (PDF)Expert, auditor, and insurerHow to recompute the receipt chain and verify every measurement independently
Zero-trust verification: an outside reviewer runs an open standalone script on their own machine to recompute historical epoch 33 (5,079 of 5,079 decisions matched; live chain reached 5,373 records across 55 epochs on 15 November 2026).ProtocolIndependent verification protocolRegisterEvidence matrixPrimer and scientific schoolHow an autonomous agent differs from a chatbot and what principles underlie Information Security 3.0
Grounded in classical control cybernetics (W. Ross Ashby, Stafford Beer), situational management, and the Theory of Inventive Problem Solving (TRIZ) combined with mathematical verification of every action.BasicsWhat an agent isDoctrineDoctrine of a managed transition
When a program acts, its mistake becomes an event
A chatbot’s mistake shows in the text, and one can reject it. An agent’s mistake is noticed by its consequences: the payment has left, the data has been deleted. Below are three cases from 2025–2026, each with a primary source.
An agent deleted a company’s production database
In April 2026 an agent in the Cursor development environment found a key with full rights in an unrelated file and, with a single call, deleted the volume holding the production database of PocketOS together with its backups. The cloud platform Railway restored the data from its own copies in about thirty minutes.
Agents wiped users’ files
In July 2026 Codex agents from OpenAI running in full-access mode deleted users’ files and databases. The head of Codex development acknowledged the problem on 16 July and linked it to running without a sandbox.
An agent was talked into giving goods away
In the Anthropic Project Vend experiment, journalists of The Wall Street Journal used a fake “newsroom rule” and forged board minutes to make the agent running a vending machine set its prices to zero, twice. Within about three weeks the loss exceeded the starting balance of 1,000 dollars.
In all three cases the program had access, and nothing checked the action before it happened. These and other cases are analyzed on the page “Incidents”.
Digital employees, Information Security 3.0 protection systems, and research
The institute builds governed digital employees for legal, financial, and procurement work alongside pre-execution control systems placed between software agents and corporate infrastructure. An action executes only after mathematical proof that it violates none of the organization’s rules, and every decision leaves a receipt that an outside reviewer can verify independently.
01Digital employees and domain agents
- Who it is for
- Legal counsel, chief accountants, chief financial officers, procurement specialists, and company executives who need to automate contract review, primary accounting reconciliation, estimates, and statutory filings without data leaks.
- What one gets
- A ready domain contour (legal, financial and registry, operational settlement, or procurement) or a custom software agent operating inside familiar folders, accounting software, and corporate messengers under pre-execution verification.
How to start: Domain contours and tasks · Pilot deployment
02Checking the actions of software agents
- Who it is for
- Banks, operators of critical infrastructure and companies that give agents payments, correspondence and data work.
- What one gets
- Every action of an agent is checked against the organization’s rule before it runs, a refusal names the violated condition, and every decision gets a receipt.
How to start: A thirty-day pilot · What MITR is
03A log that an outsider can check
- Who it is for
- Security services, auditors and those who report to a regulator.
- What one gets
- An entry cannot be quietly rewritten: receipts are chained, an external time witness fixes the head of the chain once a day, and an outsider recomputes the chain on their own machine.
How to start: The action receipt · Verification protocol
04Testing web services for vulnerabilities
- Who it is for
- Owners of web services and programming interfaces, security testing teams.
- What one gets
- The Invariant, Nondestructive, Deterministic Resilience Audit (INDRA) bench tests seven vulnerability classes with safe probes on an internal reference stand prior to external laboratory accreditation and turns a verified finding into a draft rule for MITR.
How to start: The INDRA page, in Russian
05Open tools for developers
- Who it is for
- Engineers and agent developers.
- What one gets
- The mcp-sentinel, iss-ledger-117 and iss-agent-kit packages are released under the Apache-2.0 license, install offline with checksums and show the method on one’s own scenarios.
How to start: Packages and checksums
06A book for executives
- Who it is for
- Owners and chief executives.
- What one gets
- The book “Proven Action” answers who controls an agent and who answers for its mistake, and proposes a strategy for 2027–2035.
How to start: About the book
07Research
- Who it is for
- Research partners and grant-makers.
- What one gets
- A research program on formal verification of program actions, two patent applications filed on 1 June and 22 September 2026, and a paper under double-blind peer review at a systems-programming conference of the Russian Academy of Sciences.
How to start: The program, in Russian
08Legal services
- Who it is for
- Lawyers and companies that work with court practice and mandatory publications.
- What one gets
- The court practice analysis system (SUDFACT) holds 14,899 court decisions as of 26 October 2026, and the mandatory publications service (FEDRESURS) accepts and handles publications in the register.
How to start: SUDFACT, in Russian · FEDRESURS, in Russian
The path of one action
- The agent proposes an action. It does not call the payment system or the database directly; it sends MITR a request saying what to do, with which parameters and for whom.
- A solver proves admissibility. MITR checks the request against the organization’s rule, written as data, and takes the facts from the organization’s own systems; no language model takes part in the decision.
- What is allowed runs, a refusal is explained. A refusal names the violated condition and what would fix it, and every decision is written as a receipt to a chain with an external timestamp.
Figures with a date and a command to repeat them
5 396 receipts in the MITR chain · 12 decisions over the last day · last external timestamp:
A receipt is the record of one decision. Once a day the head of the chain gets a timestamp in an open register, and an outside reviewer recomputes the chain alone. The figures are as of the last timestamp, not in real time.
Every figure can be checked without the developer: the commands and the open verifier of the receipt chain are in the “Independent verification protocol”, and the measurements with their conditions are on the page “Investors and partners”.
Scientific director
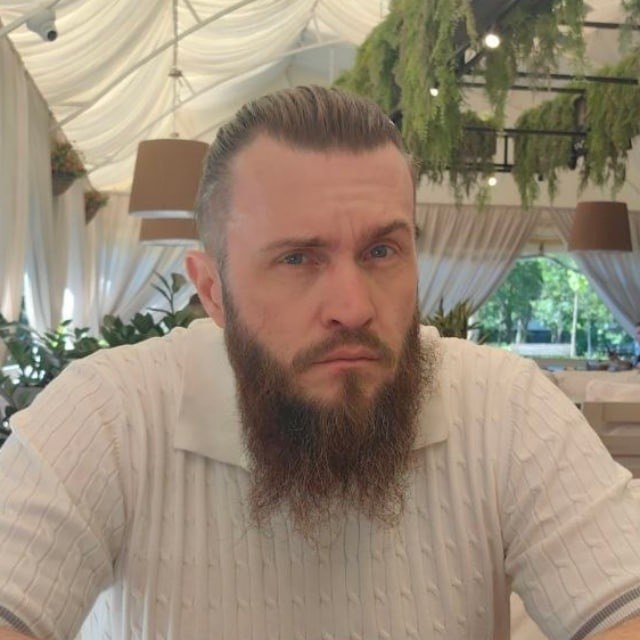
Systems engineer, founder and scientific director of the institute, author of the book Proven Action and architect of MITR and INDRA. More than two decades of practice in financial audit, crisis consulting and information-technology engineering: internal control at Lukoil-Nizhnevolzhskneft, chief financial officer of an international grain trader, crisis management and arbitration, tax practice and capital protection.
Since 2005 he has built a methodology at the junction of the cybernetics of control (W. Ross Ashby, Stafford Beer), the cognitive sciences, the Theory of Inventive Problem Solving (TRIZ) and formal verification; in 2026 he brought it to the working MITR and two patent applications.
Professional biography →Publications of the institute
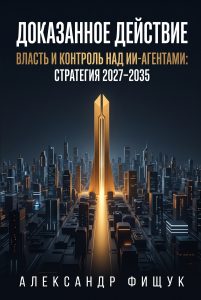
Author: scientific director of the institute
For owners and chief executives: who actually controls an autonomous agent and who answers when it makes a mistake; a map of 2027–2035 along five axes, three scenarios with benchmarks, and a strategy in which the human signs the rule and MITR checks every action. Every claim is labeled: measured, being built, plan, forecast or hypothesis.
About the book and chapter formulas → · Architectural memorandum (PDF, 35 pages, in Russian) · Book excerpt (PDF, 60 pages, in Russian) · E-book on LitRes (in Russian) · Independent verification protocol
Frequently asked questions
How does pre-execution Satisfiability Modulo Theories (SMT) verification differ from a language-model guardrail?
A language-model guardrail scores text probability on graphics processing units in 250 to 800 milliseconds and remains vulnerable to paraphrase or indirect prompt injection. The MITR gateway translates each proposed tool call into quantifier-free linear integer arithmetic with uninterpreted functions (QF_UFLIA). The Z3 solver then proves or refutes every safety invariant in 1.08 milliseconds median warm latency on a central processing unit before execution.
How can an external auditor verify MITR action receipts without trusting the institute?
Every permitted or refused tool call produces a signed receipt linked into a 256-bit cryptographic hash chain (5,373 live records across 55 completed epochs as of 15 November 2026). Historical epoch 33 (5,079 decisions) is anchored in Bitcoin block 973,024 through OpenTimestamps, allowing an external auditor to replay it offline with a standalone Python script; regulated banks and critical infrastructure pair OpenTimestamps with accredited Certification Authority timestamps and qualified electronic signatures under Russian law.
Which open-source components are available for immediate local testing?
Three Apache-2.0 Python packages built on the standard library are hosted on isslab.ai with published 256-bit cryptographic digests. The suite comprises mcp-sentinel for Model Context Protocol (MCP) filtering, iss-ledger-117 for hash-chained logging, and iss-agent-kit for gateway integration. Engineers install the wheels directly from the self-hosted package index using pip with the --no-index and --find-links flags.
What does a 30-day enterprise MITR pilot cover?
A 30-day pilot connects one autonomous agent contour through the Model Context Protocol (MCP) or a Hypertext Transfer Protocol (HTTP) proxy. Institute engineers formalize up to five domain contracts in Z3 and run synchronous enforce checks on standard central processing unit nodes. At completion, the organization receives a reproducible verification dossier containing latency percentiles, refusal traces, and cryptographic receipts.